Selecting a fleet management application involves far more than comparing features and prices. Every vehicle on the road generates personal data about identifiable drivers, which places your company squarely within the scope of the General Data Protection Regulation (GDPR). The challenge is practical: vendor brochures rarely spell out their actual safeguards, and legal clauses are often buried in annexes you receive only after signing.
The good news is that GDPR compliance can be assessed with concrete, verifiable criteria rather than legal intuition. This guide translates each major obligation into checkpoints you can apply during vendor evaluation, so you can shortlist a car fleet management app on objective grounds and avoid an expensive mistake later.
Direct answer: A GDPR-compliant fleet management app can be identified by four verifiable elements: a clear data processing agreement, documented security measures (encryption, access controls, hosting location), a defined retention policy, and transparent procedures for data subject rights and breach notification. Marketing promises alone are not sufficient evidence.
What data does a fleet management app collect?
A modern fleet management app continuously collects two intertwined streams of data: information about the vehicle and information about the person driving it. Even when a feature appears purely technical, it usually produces data that identifies, or helps identify, a specific driver.
On the vehicle side, the app typically records real-time location (GPS coordinates), routes travelled, mileage, speed, fuel or energy consumption, maintenance alerts and sometimes diagnostic data from the engine. On the driver side, it generally stores identity details, driver’s licence information, work schedules, assigned vehicles and driving behaviour indicators such as harsh braking, acceleration or idling time.
The GDPR explicitly treats this information as personal data when it can be linked to an identifiable person. Article 4(1) of the regulation lists location data among the identifiers that make a natural person identifiable. In a corporate fleet, where a vehicle is usually assigned to a named driver, location, trip and behaviour data become personal data by default.
Anonymised vs aggregated data: Only data that can no longer be linked back to an individual, even indirectly, falls outside the GDPR. A dashboard showing total fleet mileage per month is aggregated; a trip log attached to a driver’s name is not.
Consider a typical workday: a van leaves the depot at 7:12 a.m. with driver A, stops at four customer sites, idles for 22 minutes at lunch, triggers two harsh-braking events and returns at 5:48 p.m. Every one of these data points is personal data because it reveals the activity of an identifiable person throughout their working day. This is why fleet apps sit at the heart of GDPR obligations.
Which GDPR obligations apply to fleet data processing?
As the employer deploying the app, your company is the data controller: you decide why and how driver data is processed. The software vendor is usually a data processor, handling the data on your behalf under your instructions. This distinction shapes almost every obligation that follows.
Finding the right legal basis
Processing driver data requires a valid legal basis under Article 6 of the GDPR. The most common options for fleet management are:
- Legitimate interest: for example, protecting vehicles and goods, or optimising routes, provided a balancing test with drivers’ rights is documented.
- Legal obligation: for driving-time records in regulated transport activities.
- Consent: rarely appropriate in an employment context, because the imbalance of power between employer and employee limits its validity.
The European Data Protection Board, in its guidelines on connected vehicles, highlights location data as particularly sensitive and considers consent as a legal basis only in specific scenarios, such as locating a stolen vehicle. Continuous geolocation during working hours typically requires another basis and strict proportionality safeguards.
Core principles to translate into practice
Four GDPR principles shape day-to-day fleet operations:
- Lawfulness and transparency: drivers must be informed clearly about what is collected, why, and for how long.
- Data minimisation: only data necessary for the stated purpose should be collected. Permanent geolocation during breaks or outside working hours is a classic red flag.
- Storage limitation: retention periods must be defined and documented, not left open-ended.
- Security: appropriate technical and organisational measures must protect the data against loss or unauthorised access.
Alongside these principles, you must maintain a record of processing activities and ensure drivers can exercise their rights of access, rectification and, where applicable, erasure. The vendor’s documentation should make it easy for you to answer those requests.
Permanent tracking is a frequent pitfall: Geolocating company vehicles 24/7, including evenings and weekends, is generally considered disproportionate. Many data protection authorities expect the ability to deactivate tracking outside working hours when the vehicle may be used privately.
Enforcement figures show these principles are taken seriously. According to the CMS GDPR Enforcement Tracker Report (6th edition, 2025), insufficient legal basis for data processing is one of the most frequently sanctioned categories of GDPR violations across Europe, with hundreds of fines recorded since 2018.
Security criteria to evaluate before choosing an app
Once legal grounds are clear, the question becomes: can this vendor actually protect the data? Security is where marketing claims and technical reality often diverge. A structured grid of criteria helps compare candidates on equal terms.
Technical safeguards to verify
Ask for documented evidence, not verbal reassurance, on each of the following:
- Encryption in transit: communications between vehicle devices, mobile apps and servers should rely on current TLS versions.
- Encryption at rest: stored data (databases, backups) should be encrypted with documented key management.
- Authentication and access control: multi-factor authentication for administrators, role-based access, and the ability to restrict visibility by site or team.
- Logging and audit trails: who accessed which driver’s data, when, and from where.
- Backup and recovery: documented frequency, retention and tested restoration procedures.
Contractual and organisational guarantees
Because the vendor acts as a processor, Article 28 of the GDPR requires a written Data Processing Agreement (DPA). The DPA should specify the subject matter, duration, nature and purpose of the processing, the categories of data, your rights as controller, and the vendor’s obligations, including the use of sub-processors and the location of hosting.
Recognised certifications such as ISO/IEC 27001 provide useful signals about an information security management system, but they do not replace a GDPR assessment. Treat certifications as supporting evidence, not as proof of compliance on their own.
The following grid illustrates how two hypothetical vendors can be compared on the same basis:
| Criterion | Vendor A | Vendor B |
|---|---|---|
| Hosting location | EU data centres only | EU with sub-processor outside EEA |
| Encryption at rest | Yes, documented | Partial, not specified |
| MFA for administrators | Enforced by default | Optional |
| DPA provided before signature | Yes, standard template | On request after contract |
| Breach notification SLA | Within 24 hours | Not specified |
| ISO/IEC 27001 certification | Current certificate | In progress |
A side-by-side view makes gaps visible immediately and shifts the conversation with vendors from promises to documents.
How to structure your selection and onboarding process
A disciplined process keeps the decision defensible, both internally and if a data protection authority ever asks questions. Four phases usually cover the ground without overloading the project.
- Scope needs and data strictly required
List the operational problems to solve (route planning, maintenance, cost control, driver safety). For each one, define the minimum data set required. This specification becomes the yardstick for both features and data minimisation.
- Audit shortlisted vendors with a compliance checklist
Send the same written questionnaire to every candidate, covering hosting, encryption, access controls, sub-processors, retention and breach procedures. Compare answers side by side rather than demo by demo.
- Formalise the contractual framework
Review and negotiate the DPA, confidentiality clauses, service levels for incident response and conditions for data return or deletion at contract end. Involve your Data Protection Officer or legal counsel before signature.
- Inform drivers and configure the tool
Update the privacy notice given to drivers, consult employee representatives where required, and configure the app with the agreed settings: deactivation outside working hours, access restricted to authorised managers, retention periods aligned with policy.
Each phase should produce a tangible deliverable: a requirements document, a completed audit grid, a signed DPA and a configuration record. Together they form the evidence trail that demonstrates accountability under the GDPR.
Key questions to ask before signing
By the time negotiations reach the final stretch, you need pointed questions that reveal whether a vendor’s compliance posture is mature or improvised. The checklist below groups them by theme so each can be answered in writing by the vendor and attached to the contract file.
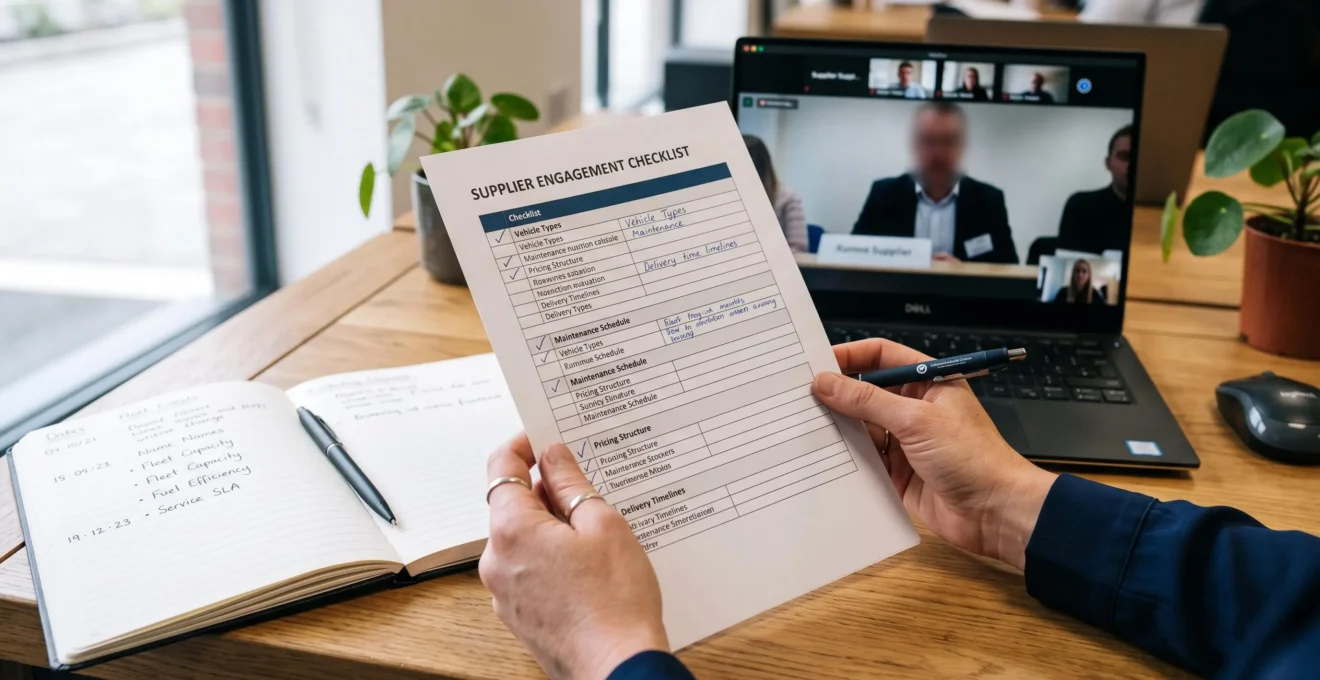
Vendor questionnaire — essentials to cover before signing
- Where exactly is driver data hosted, and who are the sub-processors?
- How is data encrypted in transit and at rest, and who manages the keys?
- What is the DPA scope, and does it reflect Article 28 requirements?
- How are personal data breaches detected, documented and notified?
- What happens to our data at contract termination: export, deletion, timeline?
Hosting, encryption and sub-processors
- In which countries are the servers hosting driver data physically located?
- Which sub-processors are involved, and are any outside the European Economic Area?
- If transfers outside the EEA occur, which safeguards apply (standard contractual clauses, supplementary measures)?
- What encryption standards are used in transit and at rest, and how are keys managed?
Contractual role and DPA
- Does the vendor explicitly accept the role of data processor under Article 28?
- Is a standard DPA provided before contract signature, and is it negotiable?
- How are instructions from the controller documented and acknowledged?
- What audit rights does the controller have, and under which conditions?
Breach management and retention
- What is the committed notification timeframe in case of a personal data breach?
- What information is included in the initial breach notification?
- What are the default retention periods for location, trip and behaviour data, and are they configurable?
- How are deletion requests from drivers handled operationally?
Portability and end of contract
- In which formats can data be exported during and at the end of the contract?
- What is the timeline for full deletion of data after termination, including backups?
- Is a written certificate of deletion provided?
- Who bears the cost of migration or export at contract end?
Any vendor serious about compliance should answer these questions in writing without hesitation. Vague answers, deferral to later stages or reluctance to share the DPA before signature are themselves signals worth noting in your evaluation.
How can a fleet manager assess GDPR compliance without legal expertise?
You do not need to be a lawyer to assess compliance in practice. Translate each GDPR obligation into a verifiable question — hosting location, encryption, DPA, retention, breach notification, access rights — and request written answers and supporting documents from each vendor. Involve your Data Protection Officer or external counsel for final review of the DPA, but the comparative evaluation can be led by the fleet or IT team using a structured checklist.
Where should fleet driver data be hosted to stay GDPR-compliant?
Hosting within the European Economic Area generally simplifies compliance because no international transfer safeguards are required. Hosting outside the EEA is possible but requires appropriate transfer mechanisms such as standard contractual clauses, together with a transfer impact assessment. Ask the vendor for the full map of hosting locations and sub-processors, including backup sites.
What security guarantees should a fleet management contract include?
At a minimum, the contract and its DPA should cover: encryption of data in transit and at rest, access control with authentication requirements, logging of administrative actions, breach notification timeframes, use and location of sub-processors, retention periods, portability and deletion at contract end, and audit rights for the controller. Recognised certifications such as ISO/IEC 27001 can usefully complement these clauses.
Is permanent vehicle geolocation allowed under the GDPR?
Continuous geolocation of company vehicles is generally considered disproportionate, especially outside working hours or when the vehicle may be used privately. The EDPB guidelines on connected vehicles stress proportionality and the sensitivity of location data. In practice, geolocation should be limited to working hours, justified by a specific purpose, documented in the record of processing activities and communicated transparently to drivers.
GDPR compliance in fleet management is less about mastering legal texts than about demanding evidence. A short, structured checklist applied uniformly to every vendor will usually reveal more than hours of product demos. Build your questionnaire, ask for documents in writing and keep the answers in your contract file — that single discipline is often what separates a defensible decision from a costly one.